
Bridging the Gap Between Cybersecurity Education and GRC Industry Needs
An Academic–Industry Perspective from PSUT
By Ali Al-Haj
Professor of Cybersecurity and Computer Engineering
Cybersecurity education has made impressive progress over the past decade. Universities now offer specialized degrees, advanced labs, and strong technical foundations. Yet a persistent concern remains across consulting firms, audit practices, and security leadership teams:
“Many cybersecurity graduates are technically capable, but not fully prepared for Governance, Risk, and Compliance (GRC) roles.”
This gap is not accidental. It reflects a structural disconnect between how cybersecurity is traditionally taught and how cybersecurity is actually practiced in organizations—where governance, risk management, and compliance shape almost every security decision.
From my experience teaching cybersecurity and developing academic programs at Princess Sumaya University for Technology (PSUT), this challenge is real—but it is also solvable.
What We Observed at PSUT
At PSUT, several signals highlighted this gap:
- Employer feedback on graduate readiness
- Student uncertainty during capstone projects and internships
- Alumni reflections from their early professional years
Technically, students performed well. Conceptually, many struggled with:
- Risk ownership and accountability
- Governance structures and decision-making
- Compliance beyond checklist thinking
This led to a key realization: “Producing strong cybersecurity graduates requires more than technical depth—it requires GRC literacy”
From my experience teaching cybersecurity and developing academic programs at Princess Sumaya University for Technology (PSUT), this challenge is real—but it is also solvable.
Moving Beyond a Single GRC Course
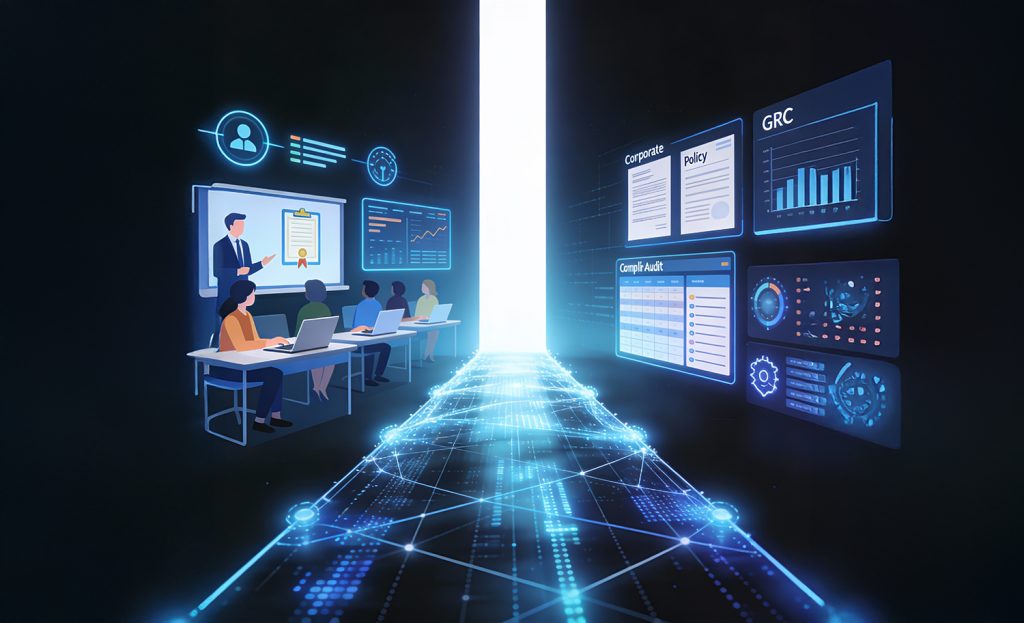
Rather than treating GRC as a standalone or “non-technical” topic, PSUT adopted a broader integration approach that combined curriculum design, industry partnership, and student engagement. A central pillar of this approach was partnering with ISACA, a global leader in GRC frameworks, professional certification, and standardization. This partnership helped anchor GRC education in:
- Real-world frameworks used by industry
- Practical governance and risk concepts
- Professional expectations beyond academia
Establishing the ISACA Student Group at PSUT
To reinforce this integration beyond the classroom, PSUT established an ISACA Student Group, which became a powerful driver of cultural change over multiple years. Over a four-year period, the student group’s primary activities included:
- Inviting GRC practitioners, auditors, and consultants to campus
- Hosting talks focused on real industry roles in governance, risk, audit, and compliance
- Exposing students to career paths they had not previously considered
- Demonstrating how GRC operates in practice—not just in textbooks
These engagements had a clear and measurable impact. Students began to see GRC not as “non-technical overhead,” but as:
- A legitimate cybersecurity career path
- A bridge between technology and leadership
- A domain where strong analytical and communication skills matter
Curriculum Impact: Student-Driven Demand
One of the most telling outcomes was what happened next. Motivated by industry exposure, many students actively chose technical electives focused on GRC-related areas, including:
- IT Governance and Management (COBIT-based)
- IT Risk Management
- IT Audit
- Cybersecurity Audit
These courses required students to analyze risk, justify controls, and communicate findings—skills directly aligned with industry needs. This demonstrated a critical insight: “When students understand why GRC matters, they actively seek it out.”
Why This Matters for Industry?
Organizations often struggle to find entry-level professionals who can bridge technical security and business decision-making. Graduates exposed early to GRC concepts are better prepared to:
- Operate in consulting and audit environments
- Communicate effectively with non-technical stakeholders
- Understand regulatory and compliance pressures
- Contribute to resilience, not just incident response
This benefits employers, graduates, and the broader cybersecurity ecosystem.
A Shared Responsibility
Closing the cybersecurity–GRC gap requires collaboration:
- Universities must embed GRC across curricula and partner with professional bodies
- Industry must engage with education early and clearly articulate expectations
- Students must view GRC as a core cybersecurity career path, not a fallback
Final Thought
Cybersecurity today is defined not only by technology, but by governance, risk awareness, and trust. PSUT’s experience shows that when GRC is integrated through curriculum, professional partnership, and student engagement, cybersecurity education becomes far more aligned with real industry needs. Bridging this gap is not optional; it is rather essential for preparing the next generation of cybersecurity professionals.
Encouragingly, this academic–industry alignment is already taking shape in Jordan. IT Security C&T, and other cybersecurity firms, have emerged as regional leaders in GRC training and professional development, playing a critical role in translating governance, risk, and compliance frameworks into practical, industry-ready skills. Through their training programs and active partnerships with Jordanian universities, these such firms contribute directly to preparing graduates and professionals who understand not only cybersecurity technologies, but also the governance and risk contexts in which those technologies operate. Such collaborations exemplify how industry and academia can work together to close the cybersecurity–GRC gap and strengthen the region’s overall cyber resilience.