
We handle security so you can handle your business.
Cybersecurity consulting, managed security, and training focused exclusively on information and cyber security, serving government, financial, and academic institutions across the MENA region.
Who We Are
“Deliver premium consultation, training, and solutions based on international standards and best practices, with emphasis on knowledge transfer and implementation ease.”
A GRC platform built from real audit work, not a generic template.
Designed by cybersecurity consultants, ExceedGRC automates compliance assessments, manages risk, tracks remediation, and measures cybersecurity maturity through a centralized dashboard.
What the platform covers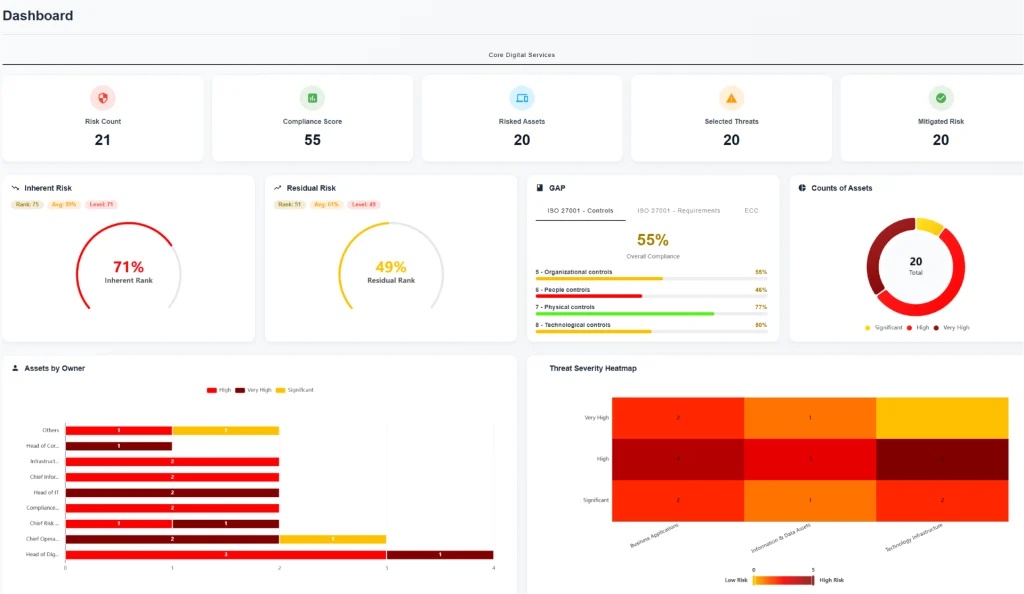
Seven service lines, one firm.
From policy-level advisory through to an always-on security operations service. Scroll to see how the work is segmented.
Strategic Consulting
Business continuity, compliance, data classification, information security management, and third-party risk, the policy layer that comes before anything gets tested.
Learn more →Infrastructure Security
Compromise assessments, architecture and configuration reviews, infrastructure penetration testing, baseline standards, vulnerability assessment, and red teaming.
Learn more →Applications Security
Mobile application penetration testing, source code review, and web application vulnerability assessment & penetration testing.
Learn more →Security Operations
SOC framework development and SOC operations assessment, building and grading the detection function itself.
Learn more →Solutions
NDR, SIEM, the ExceedGRC platform, network broker, vulnerability management, and web application assessment, packaged technology, not just advice.
Learn more →Managed Security Services
Advanced threat hunting, security monitoring, incident response retainers, and compromise assessments, delivered as an ongoing service, not a one-time report.
Learn more →Academy
Certification training and cohort-based programs, delivered with (ISC)², EC-Council, BSI, CompTIA, and ISACA.
Learn more →
Evidence, not adjectives.
Scope
Targets, boundaries, and success criteria agreed before any work starts.
Assess
Testing against the environment, or gap analysis against the standard.
Evidence
Every finding written up with reproduction steps and its business impact.
Close
Retest, internal audit, or certification support until the finding is shut.
Training Schedule
Check out our latest training courses and learn from our qualified cybersecurity instructors.
News
IT Security C&T Insights-Newsletter of 2026 Q1
IT Security C&T Insights The Quarterly Cybersecurity Newsletter of 2026 Q1 Welcome to the Q1 2026 edition of IT Security C&T ...
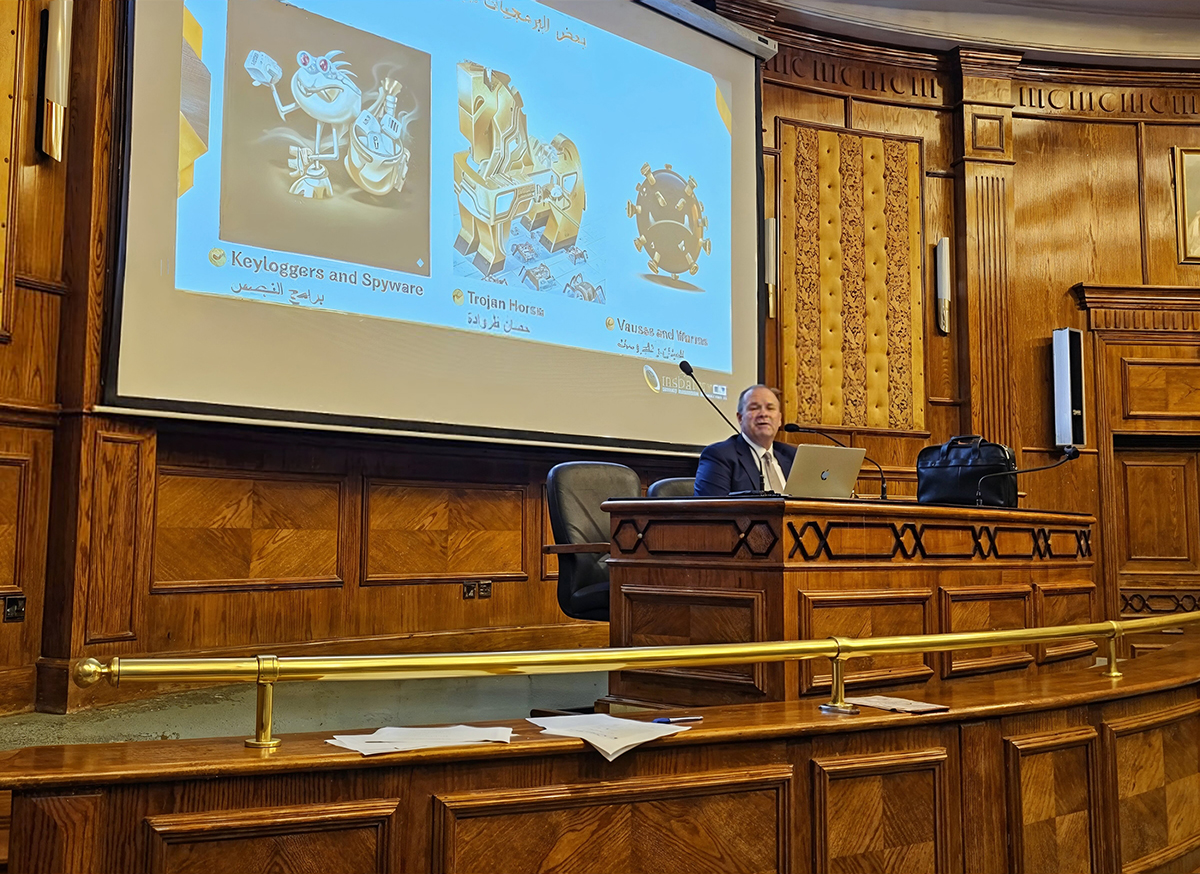
Empowering Leadership with Cybersecurity Insights at the Ministry of Foreign Affairs
Our company successfully delivered a specialized cybersecurity awareness session tailored for executive and administrative leadership a...
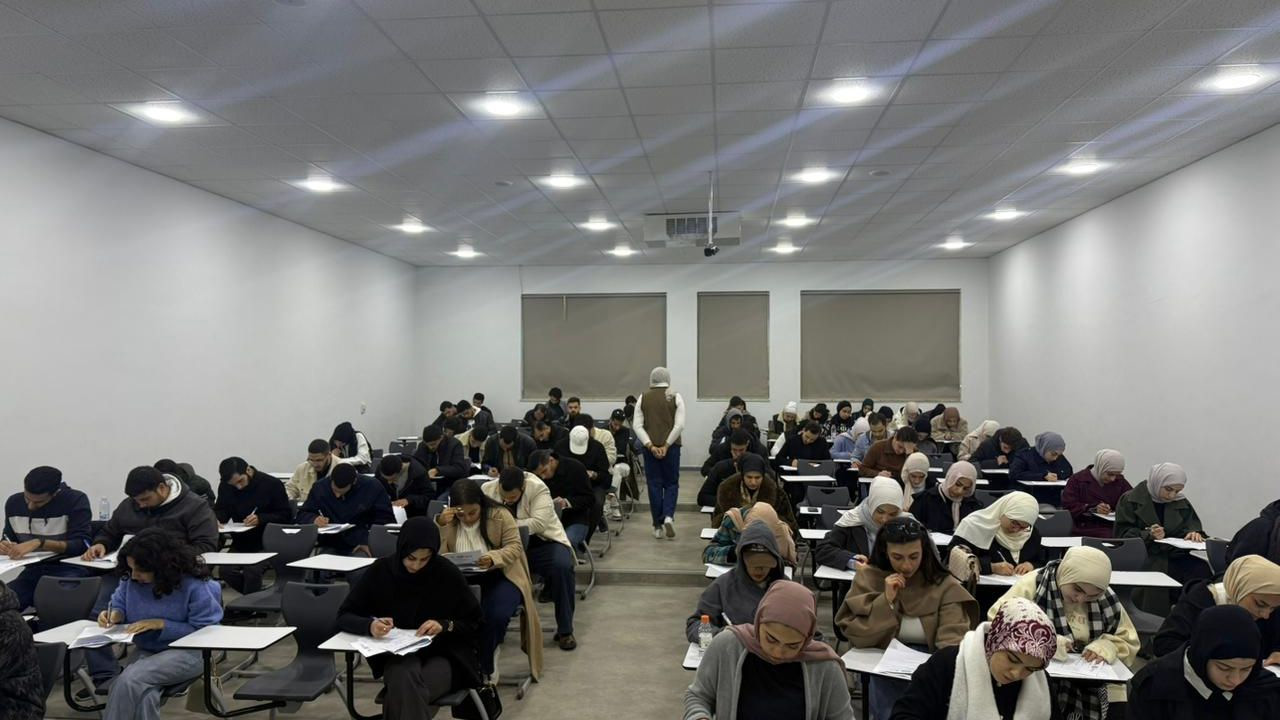
A Structured Path to Cyber Excellence
When selecting students for the Nashama Cyber Cohort, priority is never given based on registration timing.
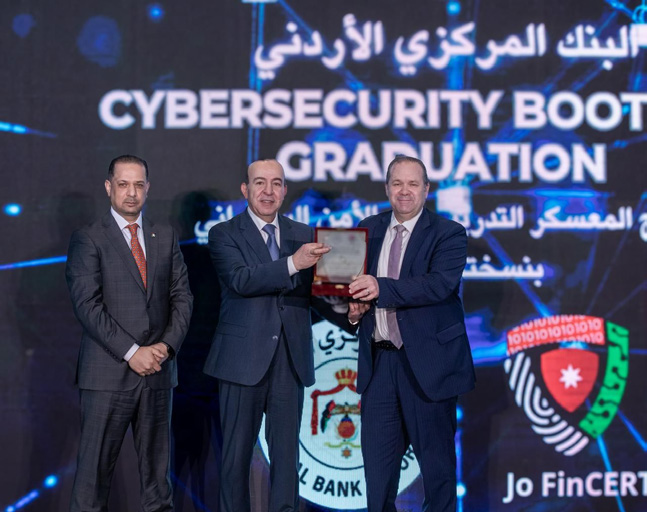
Delivery Partner of the Central Bank of Jordan’s Cybersecurity Training Camp
Proud to serve as the delivery arm for the Central Bank of Jordan’s Cybersecurity Training Camp (Second Edition – 2025) Special thanks ...
Common questions.
Where are you based, and who do you work with?
We are headquartered in Jordan, serving clients across the EMEA region, including government, financial, and academic institutions.
Do you offer both consulting and managed services?
Yes. Consulting Services cover strategic and technical advisory work, Managed Security Services deliver ongoing coverage, and Solutions are packaged technology deployments. All three can be combined.
What certifications does your team hold?
Our own ISMS is ISO 27001 certified, and our consultants and trainers hold certifications through (ISC)², EC-Council, ISACA, and CompTIA.
How do I get started?
Contact us with a short description of your need. We route the request to the right team and typically respond within one business day.