
GRC Platform (ExceedGRC)
Brings governance, risk management, and compliance, previously separate practices, into one platform. Designed by cybersecurity consultants to automate compliance assessments, manage risk, track remediation, and measure cybersecurity maturity through a centralized dashboard.
Two steps, two delivery options.
ExceedGRC runs gap and risk assessments against local and global standards including ISO 27001, NCA ECC, and SAMA CSF, and extends to any other cybersecurity framework you need to answer to.
Identify Requirements
We establish your compliance requirements, your risk acceptance level, and the rest of what shapes the configuration, then translate that into the tool so it produces gap analysis, risk assessment, and treatment reporting against your frameworks.
Implementation
Our team implements the configured platform with you, and provides support and guidance after it goes live.
Delivery options
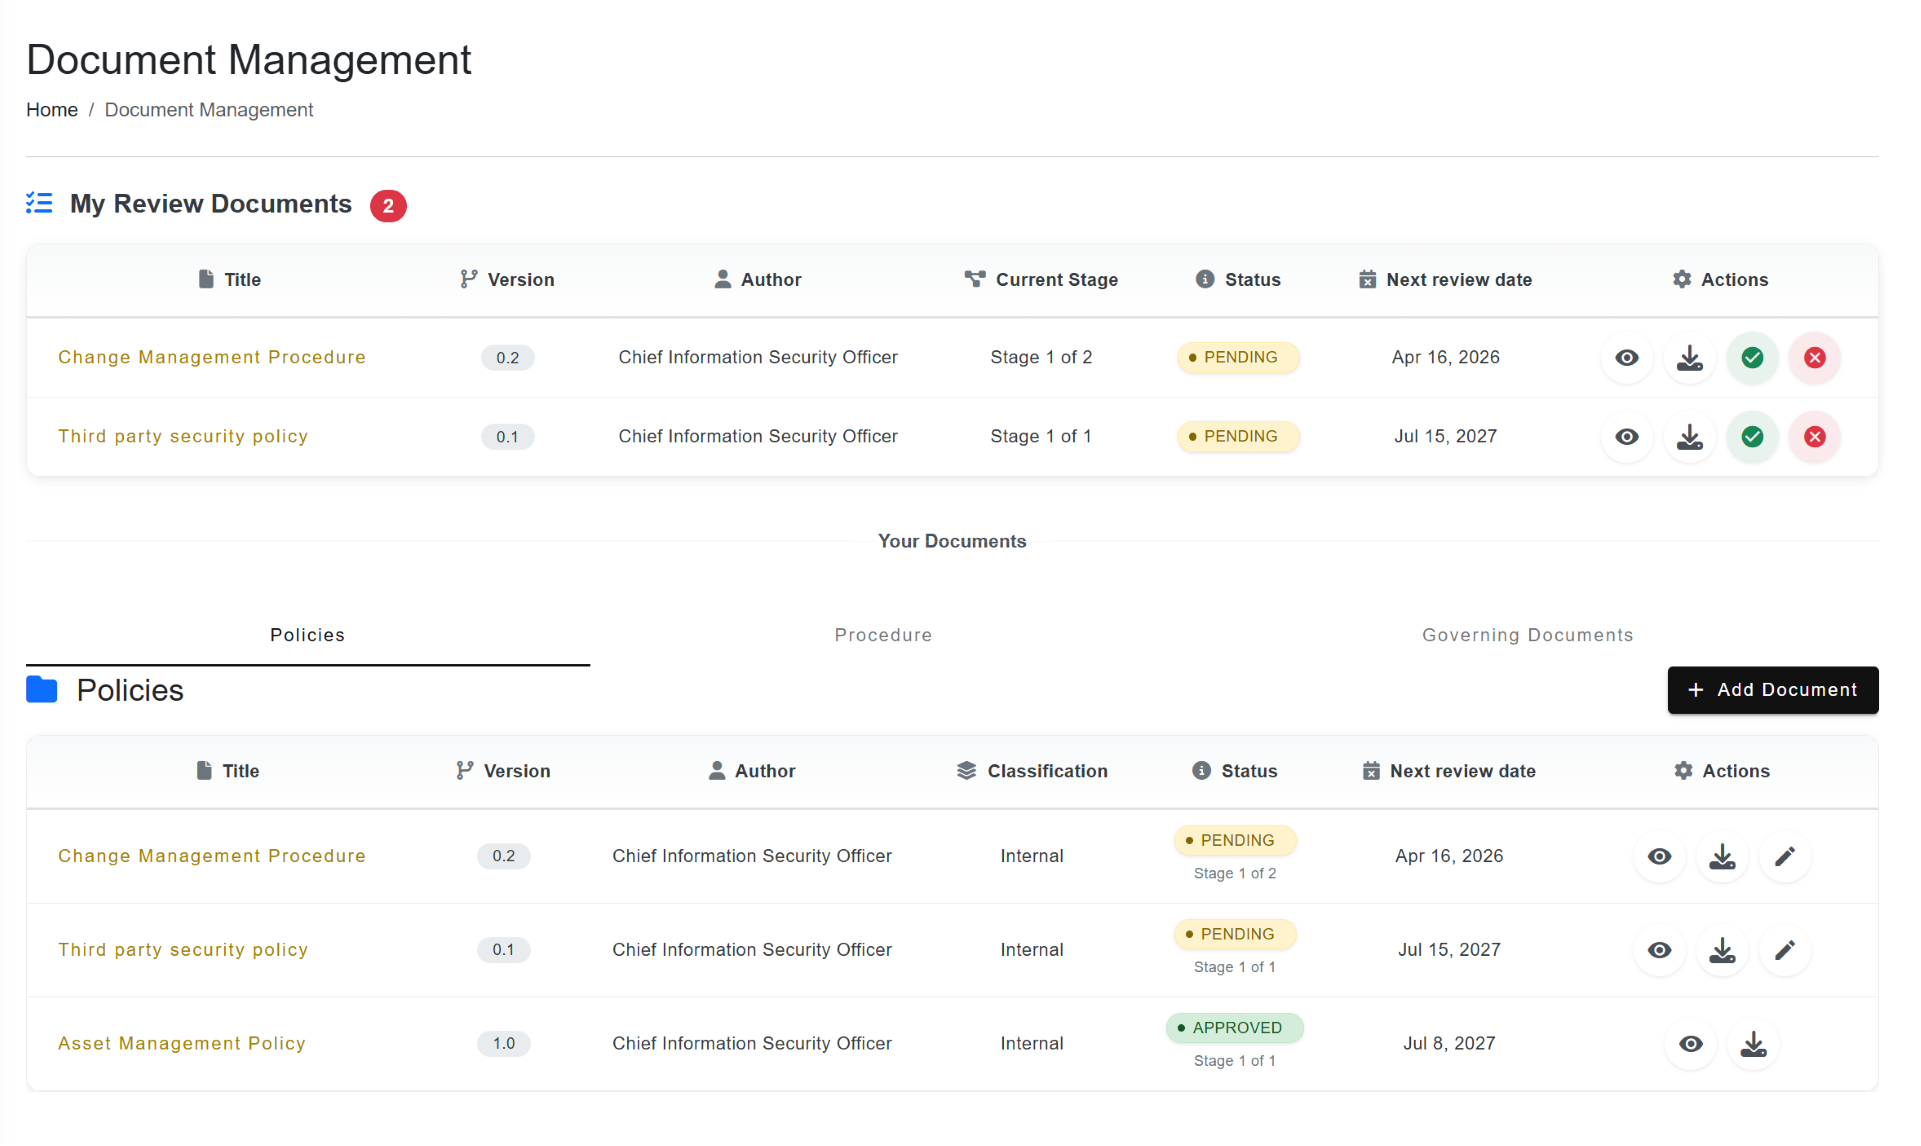
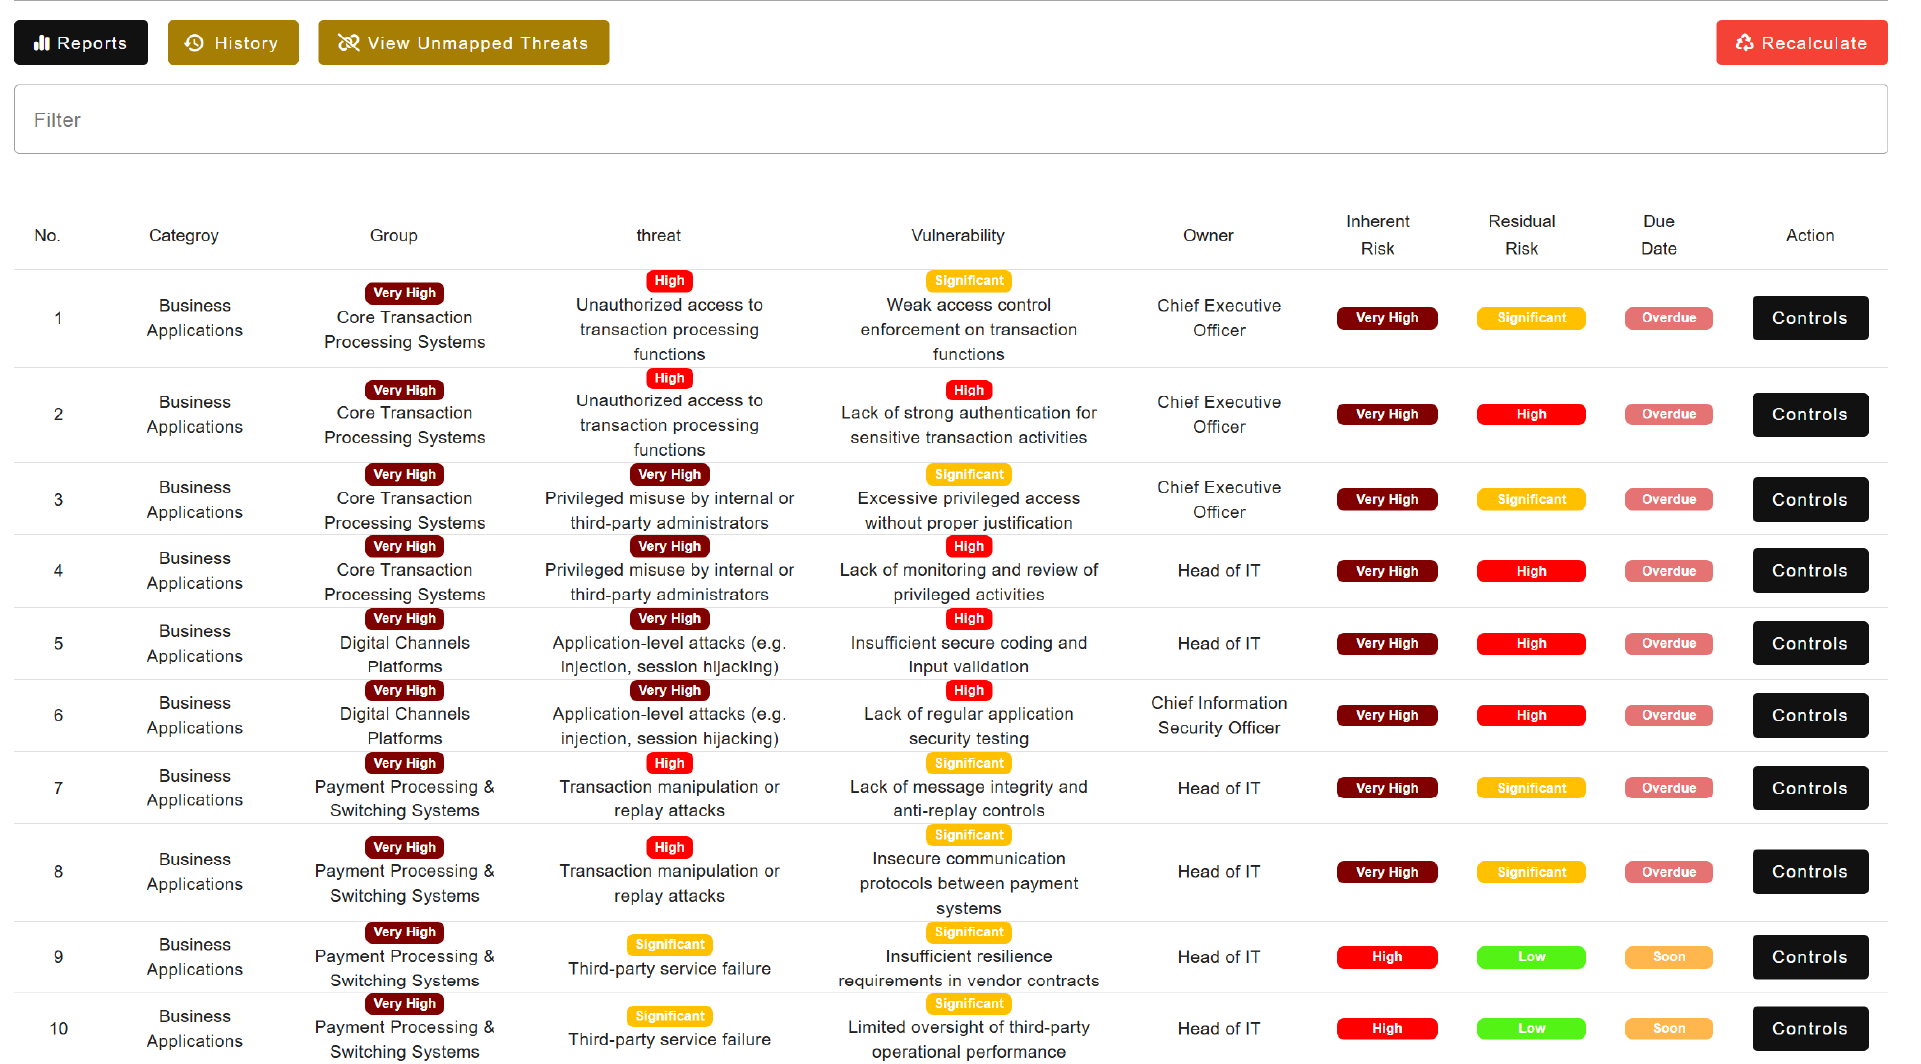
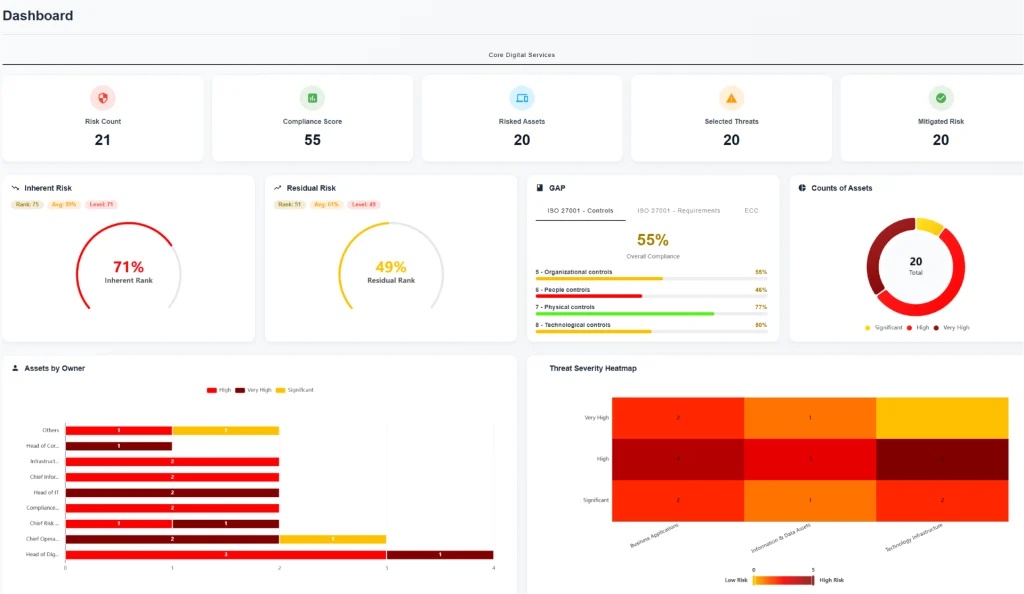
What the platform shows you.
Risk, controls and evidence in one place, reported against the frameworks you actually answer to.
Built from real audit work.
Governance, risk, and compliance used to run as separate spreadsheets and separate teams. ExceedGRC replaces that with one system consultants can actually use during an engagement.
Request a DemoWhere this connects.
Compliance
The consulting side of the same work, where a gap analysis runs to certification.
Information Security Management
The ISO 27001 system the platform tracks controls and evidence against.
Third Party Risk Management
Vendor risk assessments that need the same register and reporting discipline.
Common questions.
Which frameworks does the platform map to?
ISO 27001, SOC 2, NIST, and PCI-DSS internationally, plus regional standards including CBJ, SAMA, and NCA.
What does it actually do day to day?
Automates compliance assessments, manages risk, tracks remediation, and measures cybersecurity maturity, all through a centralized dashboard rather than separate spreadsheets.
How long until we are up and running?
Platform provisioning and access in the first week, control mapping to your frameworks across weeks two and three, then live dashboard access on an ongoing basis.
Who built it?
Cybersecurity consultants, out of real audit work rather than as a generic compliance template.